Waraxe IT Security Portal
Login or Register
October 16, 2026
Menu
Home
Logout
Discussions
Forums
Members List
IRC chat
Tools
Base64 coder
MD5 hash
CRC32 checksum
ROT13 coder
SHA-1 hash
URL-decoder
Sql Char Encoder
Affiliates
y3dips ITsec
Md5 Cracker
User Manuals
AlbumNow
Content
Content
Sections
FAQ
Top
Info
Feedback
Recommend Us
Search
Journal
Your Account
User Info
Welcome, Anonymous
Nickname
Password
(Register)

Membership:
Latest: MichaelSnaRe
New Today: 0
New Yesterday: 0
Overall: 9144

People Online:
Visitors: 1131
Members: 0
Total: 1131
Full disclosure
VestaCP <= 0.9.8-26: authenticated config-parser eval sinks ->root RCE (VESTACP-2026-001)
[SYSS-2026-080]: dcm4che - Path Traversal (CWE-22)
[SYSS-2026-079]: dcm4che - Path Traversal (CWE-22)
[SYSS-2026-078]: dcm4che - Path Traversal (CWE-22)
[SYSS-2026-077]: dcm4che - Path Traversal (CWE-22)
[0day-rubbish] Synametrics Syncrify 6.2 build 1178 authenticated PublicLink chunk-upload path traversal to /etc/cron.d and root command execution (7.5)
[0day-rubbish] South River Technologies Titan MFT Server 26.0.0 first-run administrator setup chained to job post-command injection, NT AUTHORITY\SYSTEM (8.1)
[0day-rubbish] SmartBear Collaborator Server 15.1.15101 authenticated DOORS/Simulink review-file upload zip-slip to anonymous webroot Groovy Server Page execution as uid 1001 (7.5)
[0day-rubbish] PacsOne Server 7.3.9 authenticated DICOMweb STOW-RS SOP Instance UID path traversal to www-data code execution on a PACS host (7.2)
[0day-rubbish] Maian Pal 2.1 product image upload with no extension allow-list to PHP webshell and www-data uid 33 code execution (7.2, PR:H)
[0day-rubbish] Maian Guardian 2.1 license generator projid command injection to www-data uid 33 code execution (7.2, PR:H)
[0day-rubbish] Dataedo Portal 26.2.8 with Dataedo Agent 26.2.8 unrestricted scheduler job-type deserialization to Agent-host command execution (8.1)
[0day-rubbish] CloudPanel 2.5.4-3 site-settings rootDirectory nginx virtual-host injection to host root code execution (8.8)
[0day-rubbish] Auerswald COMmander 6000 / 6000R 8.6D unauthenticated provisioning import zip-slip to root binary hijack and root code execution (9.8)
[0day-rubbish] Abyss Web Server X1 2.16.22.0 first-run console credential takeover to configuration-write log-as-CGI command execution (7.5)
Log in Register Forum FAQ Memberlist Search
IT Security and Insecurity Portal

www.waraxe.us Forum Index -> Tools -> Crawling + Finding SQL Injection with Scrawlr
Post new topicReply to topic View previous topic :: View next topic
Crawling + Finding SQL Injection with Scrawlr
PostPosted: Fri Jul 09, 2010 3:05 am Reply with quote
sEcZx
Regular user
Regular user
Joined: Jul 09, 2010
Posts: 9


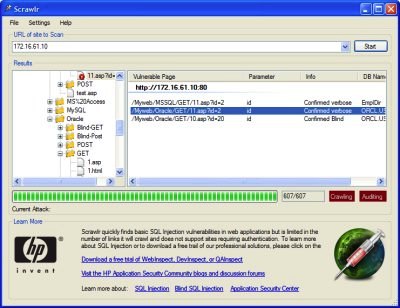
Scrawlr is the latest tool to come out of HP’s Web Security Research Group. It was built in response to the massive number of SQL injection attacks happening on the web this year. Most of these vulnerable sites are found through googling, so Scrawlr works the same way. Point it at your web server and it will crawl all of the pages and evaluate the URL parameters to see if they’re vulnerable to verbose injection. It reports the SQL server and table names if it comes across anything.

It only supports 1500 pages right now and can’t do authentication or blind injection. It’s still a free tool and a great way to identify if your site is vulnerable to automated tools finding you website via search engines

Scrawlr will crawl and audit any of the following file extensions:

•htm/html
•asp
•aspx
•php/php3/php4
•jsp
•js
•txt
•cfm
•any file without an extension


Download

https://h30406.www3.hp.com/campaigns/2008/wwcampaign/1-57C4K/images/Scrawlr.msi

Thanks .
View user's profile Send private message
Crawling + Finding SQL Injection with Scrawlr
www.waraxe.us Forum Index -> Tools
You cannot post new topics in this forum
You cannot reply to topics in this forum
You cannot edit your posts in this forum
You cannot delete your posts in this forum
You cannot vote in polls in this forum
All times are GMT
Page 1 of 1

Post new topicReply to topic


Powered by phpBB © 2001-2008 phpBB Group


PCWizardHub - Helping you fix, build, and optimize your PC life
All logos and trademarks in this site are property of their respective owner. The comments and posts are property of their posters, all the rest (c) 2004-2024 Janek Vind "waraxe"
Page Generation: 0.050 Seconds