 |
|
 |
 |
Menu |
 |
|
 Home |
| |
|
 Discussions |
| |
|
 Tools |
| |
|
| Affiliates |
| |
|
 Content |
| |
|
 Info |
| | |
|
|
|
|
|
User Info |
|
 Membership:
 Latest: MichaelSnaRe
 New Today: 0
 New Yesterday: 0
 Overall: 9144
 People Online:
 Visitors: 1420
 Members: 0
 Total: 1420
|
|
|
|
|
|
Full disclosure |
|
|
|
 |
|
 |
 |
|
 |
IT Security and Insecurity Portal |
|
|
exploit saying invaild response... help me |
|
 Posted: Mon Feb 23, 2009 1:34 am |
 |
|
| acid2k1 |
| Regular user |

 |
|
| Joined: Feb 21, 2009 |
| Posts: 15 |
|
|
|
 |
|
 |
|
hello waraxe members
ok i keep getting this error i dont know what im doing wrong
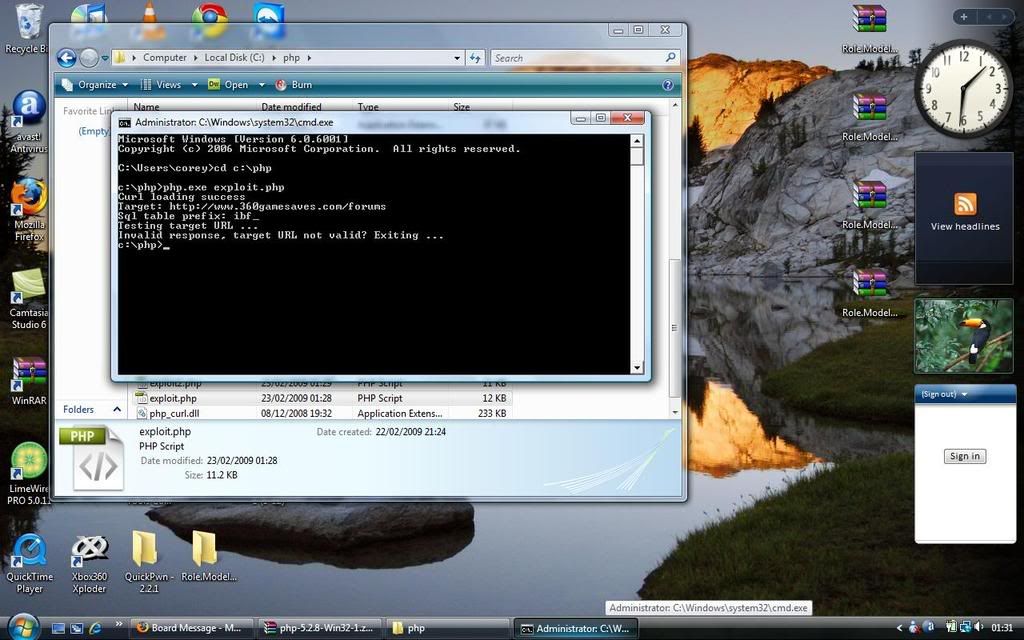
hope you can help me
thanks |
|
|
|
|
| Posted: Mon Feb 23, 2009 2:30 am |
|
|
| skmpz |
| Advanced user |

 |
|
| Joined: Oct 11, 2008 |
| Posts: 169 |
| Location: Cyprus |
|
|
|
|
|
|
|
|
|
|
| Posted: Mon Feb 23, 2009 2:50 am |
|
|
| acid2k1 |
| Regular user |
|
|
| Joined: Feb 21, 2009 |
| Posts: 15 |
|
|
|
|
|
|
|
thanks it worked what you said thanks...
but i get this error now "Target is patched"
how do i fix it.
one more question how do you find out what version the site is using like is it 2.2.x or 2.3.x etc... |
|
|
|
|
| Posted: Mon Feb 23, 2009 8:52 am |
|
|
| one23 |
| Advanced user |
 |
|
| Joined: Dec 12, 2008 |
| Posts: 98 |
|
|
|
|
|
|
|
| acid2k1 wrote: |
but i get this error now "Target is patched"
how do i fix it.
one more question how do you find out what version the site is using like is it 2.2.x or 2.3.x etc... |
So Your Target Patched And You're Not Able To Get Data
With This Exploit !
Also As skmpz Said , Hide Your Target . |
|
|
|
|
| Posted: Mon Feb 23, 2009 3:49 pm |
|
|
| acid2k1 |
| Regular user |
|
|
| Joined: Feb 21, 2009 |
| Posts: 15 |
|
|
|
|
|
|
|
| one23 wrote: | | acid2k1 wrote: |
but i get this error now "Target is patched"
how do i fix it.
one more question how do you find out what version the site is using like is it 2.2.x or 2.3.x etc... |
So Your Target Patched And You're Not Able To Get Data
With This Exploit !
Also As skmpz Said , Hide Your Target . |
ok il hide my target url in my next post sorry guys.
but you saying wrong exploit what exploit do i need to use.
thanks for the help |
|
|
|
|
| Posted: Mon Feb 23, 2009 3:58 pm |
|
|
| skmpz |
| Advanced user |
|
|
| Joined: Oct 11, 2008 |
| Posts: 169 |
| Location: Cyprus |
|
|
|
|
|
|
look.. ipb is not an easy forum to hack..
for version >= 2.3.5 i think the version was displayed at the bottom if not changed.. now if its not displayed at the bottom u can try taking a look at the source code..
 |
|
|
|
|
| Posted: Tue Feb 24, 2009 5:37 am |
|
|
| constantine9110 |
| Regular user |
|
|
| Joined: Feb 24, 2009 |
| Posts: 6 |
|
|
|
|
|
|
|
hey guys, i am still getting the same error message even after i put in the back slash "/" e.g. http://www.xxxxxx.com/forum/
can anyone help me? maybe i can PM u the link |
|
|
|
|
www.waraxe.us Forum Index -> Invision Power Board
You cannot post new topics in this forum
You cannot reply to topics in this forum
You cannot edit your posts in this forum
You cannot delete your posts in this forum
You cannot vote in polls in this forum
|
All times are GMT
Page 1 of 1
|
|
|
|
Powered by phpBB © 2001-2008 phpBB Group
|
|
|
|
|
|
|


