 |
|
 |
 |
Menu |
 |
|
 Home |
| |
|
 Discussions |
| |
|
 Tools |
| |
|
| Affiliates |
| |
|
 Content |
| |
|
 Info |
| | |
|
|
|
|
|
User Info |
|
 Membership:
 Latest: MichaelSnaRe
 New Today: 0
 New Yesterday: 0
 Overall: 9144
 People Online:
 Visitors: 1032
 Members: 0
 Total: 1032
|
|
|
|
|
|
Full disclosure |
|
|
|
 |
|
 |
 |
|
 |
IT Security and Insecurity Portal |
|
|
Crawling + Finding SQL Injection with Scrawlr |
|
 Posted: Fri Jul 09, 2010 3:05 am |
 |
|
| sEcZx |
| Regular user |

 |
|
| Joined: Jul 09, 2010 |
| Posts: 9 |
|
|
|
 |
|
 |
|
Scrawlr is the latest tool to come out of HP’s Web Security Research Group. It was built in response to the massive number of SQL injection attacks happening on the web this year. Most of these vulnerable sites are found through googling, so Scrawlr works the same way. Point it at your web server and it will crawl all of the pages and evaluate the URL parameters to see if they’re vulnerable to verbose injection. It reports the SQL server and table names if it comes across anything.
It only supports 1500 pages right now and can’t do authentication or blind injection. It’s still a free tool and a great way to identify if your site is vulnerable to automated tools finding you website via search engines
Scrawlr will crawl and audit any of the following file extensions:
•htm/html
•asp
•aspx
•php/php3/php4
•jsp
•js
•txt
•cfm
•any file without an extension
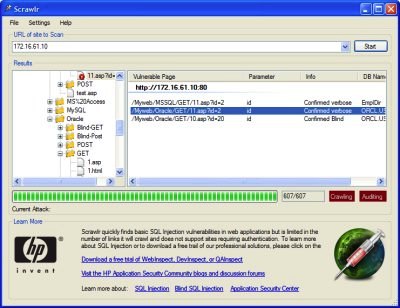

Download
https://h30406.www3.hp.com/campaigns/2008/wwcampaign/1-57C4K/images/Scrawlr.msi
Thanks . |
|
|
|
|
|
www.waraxe.us Forum Index -> Tools
You cannot post new topics in this forum
You cannot reply to topics in this forum
You cannot edit your posts in this forum
You cannot delete your posts in this forum
You cannot vote in polls in this forum
|
All times are GMT
Page 1 of 1
|
|
|
|
Powered by phpBB © 2001-2008 phpBB Group
|
|
|
|
|
|
|


